
- Binance estimates a security breach at about $6.3 billion, which would make it the largest crypto heist on record. The exchange has suspended all deposits and withdrawals.
- About $3 billion has been frozen on-chain, including assets blocked by Tether and Circle. Freezing stops the money from moving, but recovery needs a separate legal process that can take months or years.
- Binance’s early findings point to a compromised DevOps engineer’s laptop, and it has found no evidence of a wallet private-key leak. It has pledged to cover all losses from its SAFU fund and company reserves.
- TRM Labs and Chainalysis attribute the attack to North Korea’s TraderTraitor group. Binance has not named an attacker, and no government has confirmed the link.
Binance, the world’s largest cryptocurrency exchange, has suspended all deposits and withdrawals after a security breach it estimates at about $6.3 billion. If confirmed, it would be the biggest crypto theft on record.
The company says roughly $3 billion has been frozen on-chain, and its early investigation points to a compromised engineer’s laptop. Blockchain intelligence firms TRM Labs and Chainalysis attribute the attack to North Korea’s TraderTraitor group, but Binance has not named any perpetrator.
What Binance Has Confirmed
Binance is a crypto trading platform where users buy, sell and trade digital assets. It was founded in China in 2017 by Changpeng Zhao, who remains its largest shareholder. According to CoinMarketCap, it holds about $155 billion in assets under management, more than any other exchange.
Binance’s initial investigation suggests that the security incident may involve a compromised DevOps engineer’s laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions. We have found no evidence of any wallet private key leak. We will share a detailed technical post-mortem once the investigation is complete and the facts are fully verified.
The estimated total impact sits at around $6.3B. We have worked with blockchain partners to freeze affected assets, with ~$3 billion frozen on-chain so far.
Binance will cover all losses from the SAFU fund and the company’s funds. User funds are safe. We will also publish an updated Proof of Reserves once the remediation is complete.As an immediate precaution, Binance has:
– temporarily suspended deposits and withdrawals while security checks are completed;
– revoked the affected address authorisation;
– engaged law enforcement and blockchain intelligence partners to trace and recover funds.Our teams are working around the clock to resolve this issue safely and thoroughly. We are working closely with our law enforcement partners to confirm the identity of these criminals and bring them to justice.
Please rely only on official Binance channels for updates. Please feel free to contact Binance Customer Support if you have any further questions.
https://t.co/ywB2mKFy0p
— Binance (@binance) October 30, 2026
The company said unauthorized outflows were detected from its hot wallets across multiple blockchains, including Ethereum, Bitcoin and Tron. A hot wallet is a crypto wallet that stays connected to the internet. That makes it convenient for everyday transactions but more exposed to attacks.
Binance temporarily halted deposits and withdrawals while it carries out security checks. About $3 billion of the affected assets has been frozen on-chain with help from blockchain partners. The status of the remaining funds is still under review. Binance.US, the company’s separate US platform, was not affected.
Update: The current verified total frozen amount is around $3 billion.
Our teams continue to work closely with law enforcement, issuers, blockchain intelligence firms and industry partners to trace and freeze additional assets.
We will only share confirmed figures and will provide further updates as more verified information becomes available. User funds are safe.
— Binance (@binance) October 30, 2026
Zhao said earlier that the exchange appeared to have been hacked. Binance itself has described the event as a “security incident.”
User funds are SAFU!
Yet, this pregnant lady 👇 pulled an all nighter, along side hundreds of Binancians.
Many industry friends and even competitors (including some previously-not-so-friendly ones) provided very much needed help. 🙏
It hurts, but we will survive. 💪
— CZ 🔶 BNB (@cz_binance) October 30, 2026
How The Attack Appears To Have Started
In its official update on October 30, Binance said its initial investigation suggests the breach may have begun with a compromised DevOps engineer’s laptop. DevOps is the team that handles both software development and IT operations.
According to the exchange, the attacker used that access to reach a service container and submit unauthorized withdrawal transactions. Binance said it has found no evidence that any wallet private keys were leaked.
The company will publish a detailed technical post-mortem once the investigation is complete and the facts are verified.
Binance Says It Will Cover All Losses
Co-founder Yi He said user funds remain safe. Binance has pledged to cover all losses through its Secure Asset Fund for Users (SAFU) and company reserves, ensuring that affected users will not bear the financial impact.
Binance will cover all losses.
As a precaution, all deposits and withdrawals are temporarily suspended while our team conducts security checks, freezes funds, and works with law enforcement.
We are working around the clock and will share a full post-mortem once the investigation is complete. Please rely only on official Binance channels for updates.
— Binance (@binance) October 30, 2026
A Binance representative repeated those assurances and pointed to the exchange’s latest official statement for updates. “We have teams working day and night to ensure we fully and safely resolve this issue. We are also working closely with our law enforcement partners to identify these criminals and bring them to justice,” it said in a separate statement.
Tether & Circle Help Freeze Stolen Funds
The frozen assets include funds blocked by stablecoin issuers Tether and Circle. Tether issues the USDT stablecoin, and Circle issues USDC. Both can freeze tokens at specific blockchain addresses, which helped investigators hold part of the stolen funds in place. Binance says it is working with law enforcement and industry partners to trace the remaining assets.
Can Frozen Funds Be Recovered?
Freezing and recovering are two separate steps. Ari Redbord, global head of policy at blockchain intelligence firm TRM Labs, is a former US federal prosecutor and Treasury official. He said: “A freeze stops the money from moving, and recovery follows through legal process.”
Redbord said law enforcement typically obtains a court order or seizure warrant before working with stablecoin issuers to release or reissue assets and return them to their rightful owners. He described stablecoins as “the most recoverable asset class in crypto because the issuer controls the token contract.” Tether and Circle can freeze, burn and reissue tokens, which allows frozen USDT and USDC to be returned to a victim.
Bitcoin and ether are harder to recover because no issuer can directly freeze them. Investigators must instead trace the funds through exchanges and other crypto services where they can potentially be intercepted.
Eric Jardine, head of research at blockchain analytics firm Chainalysis, said returning frozen assets requires coordination among law enforcement, exchanges and token issuers. “There is no standard recovery timeline,” he said. “A technical freeze may happen quickly, while returning funds can take months or years.”
Jardine added that bitcoin and ether, although they cannot be frozen by an issuer, can still be traced on public blockchains. Investigators can intervene when the funds reach a cooperating exchange or another centralized platform.
Musk Says AI Agents Could Repeat the Binance Exploit Strategy
Elon Musk has responded to the ongoing Binance hot-wallet exploit, which is estimated to have had a ~$6.3 billion impact. He warned that superintelligent AI agents will eventually run the same DeFi play on their own. The method involves depositing stablecoins that issuers can freeze as collateral, in this case $60 million in USDT on Aave.
The borrower then takes out assets that cannot be frozen, here about 19,762 WETH (roughly $45 million), and secures the funds before issuers can act. “Super intelligence agents will at some point do this to gain currency for themselves, not a human,” Musk wrote.
@cryptoblaney Super intelligence agents will at some point do this to gain currency for themselves, not a human
— Elon Musk (@elonmusk) October 30, 2026
Tether and Circle have already frozen billions of dollars, and Aave has restricted markets across multiple chains. Binance says user funds are covered and that roughly $3 billion has been frozen so far.
Analysts Point To North Korea’s TraderTraitor Group
Two blockchain intelligence firms say the same North Korean unit behind the Bybit hack is responsible. Crypto Exchange Bybit was hit with an $1.5 billion loss in February 2025. The FBI said the attack was carried out by a group called TraderTraitor. The group has been linked by investigators to the Lazarus Group, a state-sponsored cybercriminal group based in North Korea.
Source: trmlabs.com
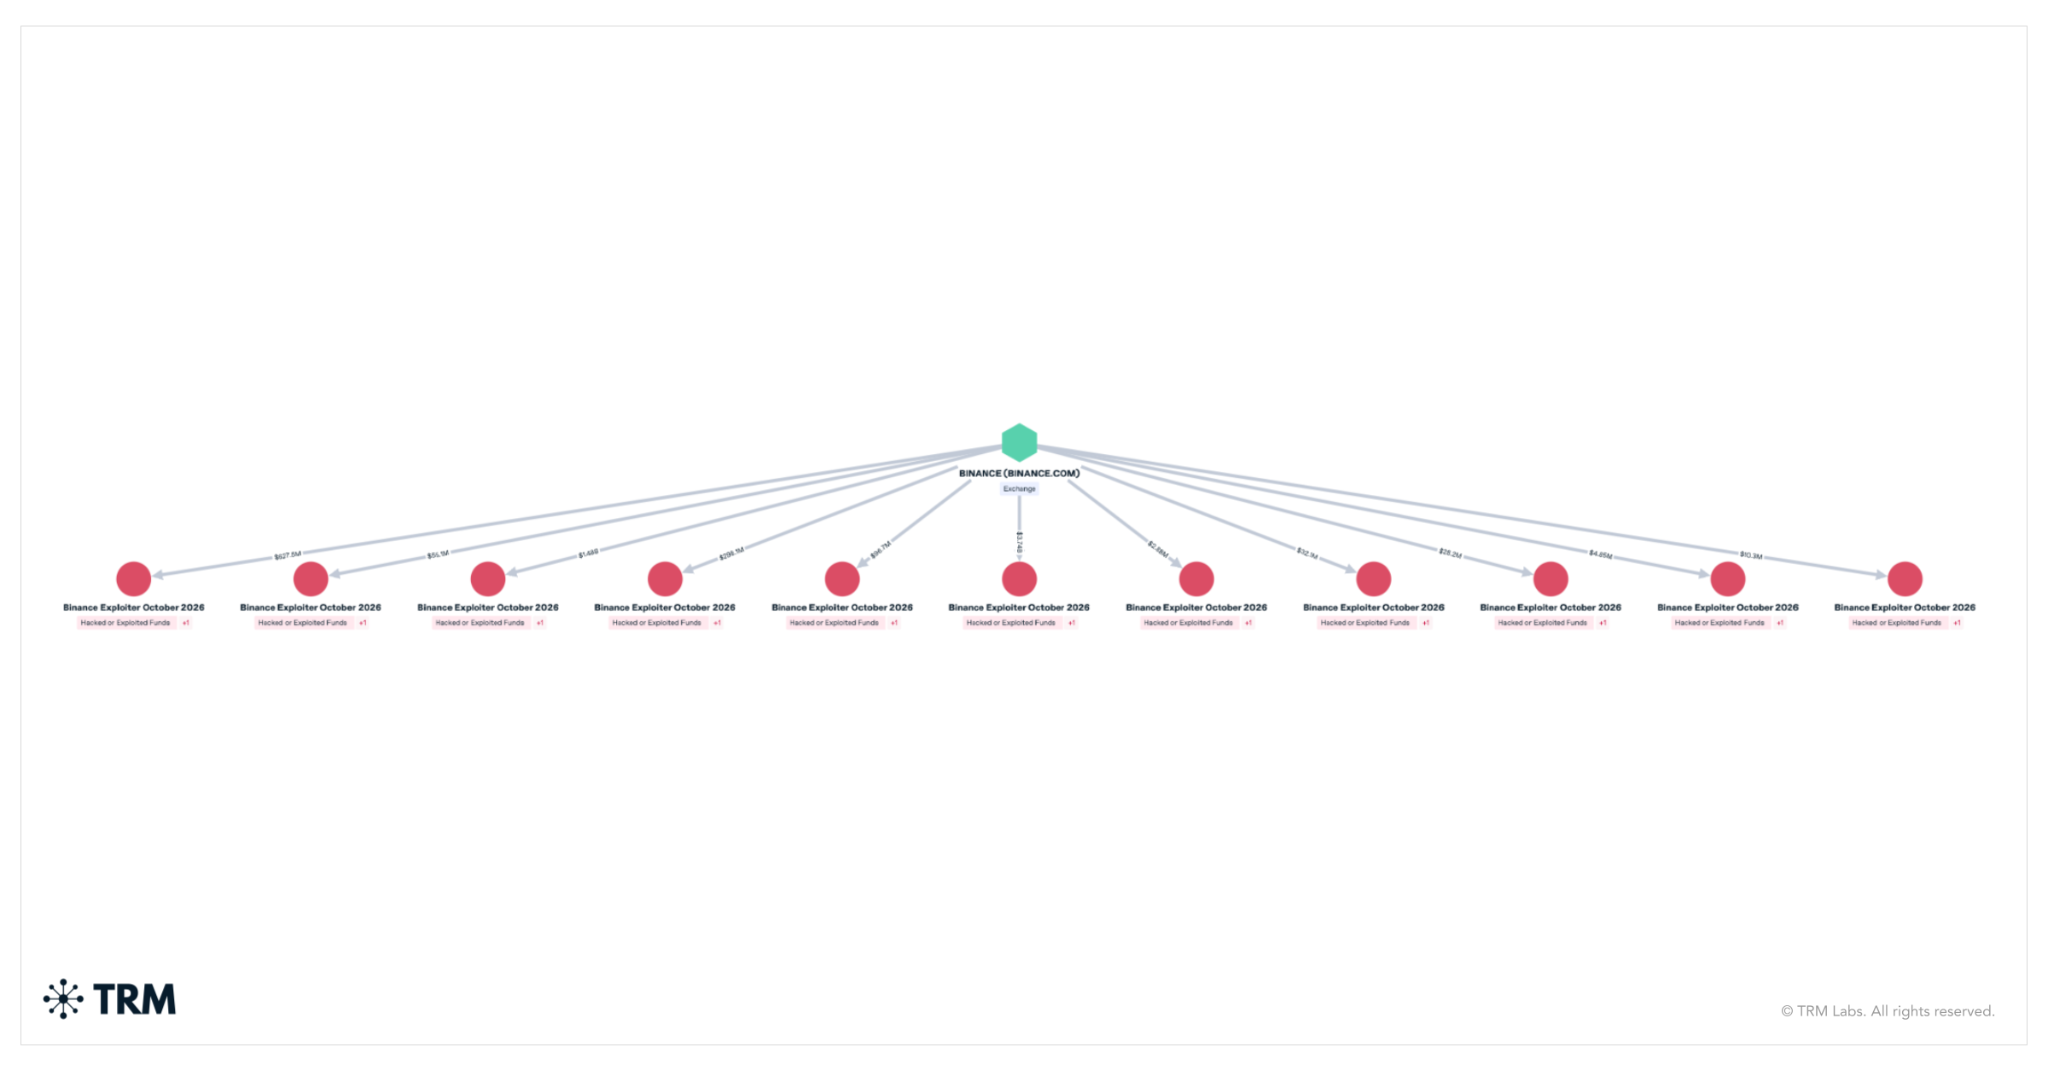
TRM Labs assesses with “high confidence” that TraderTraitor carried out the October 29 attack, citing “robust on and off-chain intelligence.” Chainalysis co-founder and CEO Jonathan Levin said the firm assesses the hack, which he put at $6.4 billion, was likely carried out by the same group, citing links to previous attacks. The attribution rests on on-chain patterns that match the Bybit attack and other past incidents.
If confirmed, it would be North Korea’s largest crypto theft to date. At TRM’s figure of about $6.36 billion, it is roughly four times the size of Bybit, which held the previous record. Binance has not named an attacker, and no government has confirmed the link.
Redbord called the attack “unprecedented” and a “watershed.” He said: “When North Korea steals at this scale, the money funds weapons proliferation and other destabilising activity. That makes this a global security issue, not just a crypto theft.”
How The Theft Was Carried Out
TRM Labs said the attack shared several traits with earlier North Korea-linked incidents. These include preparations made well before the theft and transaction signatures obtained in advance.
We live in unprecedented times. But DPRK are up to their old tricks. We assess @binance hack for $6.4B was likely done by DPRK group TraderTraitor due to links to previous hack. Industry partners have already frozen ~$3B and we @chainalysis continue to follow all of the funds https://t.co/9WiT5IZWbG
— Jonylevin (@jony_levin) October 30, 2026
By TRM’s estimate, about $6.36 billion in digital assets was moved from Binance wallets across 10 blockchains. Most of it was transferred within about 20 minutes. The firm said preparations began at least 36 hours before the theft, with the attackers using Tornado Cash, a cryptocurrency mixing service that obscures the origin of funds, to fund their wallets ahead of the breach.
Onchain Trails Link The Theft To Bitget & Phemex
Independent blockchain investigator ZachXBT said funds from the Binance hack and the $388 million Bitget exploit were commingled at address 0x151…feb7, about 45 minutes before his 04:51 UTC post. The funds arrived through THORChain, a decentralized protocol for swapping assets across blockchains. He said this shows “the same actor is likely behind both incidents.”
Update: Stolen funds from the $6.3B Binance exploit and $388M Bitget exploit were commingled at the same address 45 minutes ago, after arriving via THORChain.
This indicates the same actor is likely behind both incidents.
The Bitget exploit was attributed to DPRK-linked TraiderTraitor, which had overlap with other previous exploits such as Kelp DAO.
Commingling address:
0x15104a9ce0f08a8f0075a0869ae80e795fe0feb7Bitget exploit context: https://t.co/6S31Kwc3HI
— ZachXBT (@zachxbt) October 30, 2026
Bitget, a Seychelles-based centralized exchange, lost funds from its hot and warm wallets in a September 24 breach. ZachXBT noted that the Bitget exploit had been attributed to TraderTraitor, a group linked to the Democratic People’s Republic of Korea (DPRK), commonly called North Korea. He added that the group’s activity overlapped with earlier attacks, including the Kelp DAO exploit.
Blockchain analytics firm MistTrack found a separate connection. It traced TRX, the native token of the Tron network, stolen from Binance through four Tron addresses: TG5iBM…wvzsGi, TRBdW…PRki, TUoVs…EK6eM and TMfBq…AyQxY. The funds then entered Bitget Wallet’s swap bridge and crossed to Ethereum address 0xCd68…3396.
MistTrack said the same destination address appeared in earlier flows tied to the hacker behind the Phemex exchange theft. Those earlier funds had passed through wallets including 0x17bcc…862631, 0x140de…89661f, 0xc4342a…5e593, 0x1dc3…de27f and 0x60628…0fcf89 before reaching the shared endpoint.
MistTrack described this as verifiable on-chain evidence that the Binance TRX proceeds and the earlier Phemex funds converged on one wallet during laundering. Analysts will be watching this address for any further developments. Often, these types of malicious actors will target the same bridging tools and locations.
Neither ZachXBT’s finding nor MistTrack’s is a formal attribution. A shared address shows that stolen funds converged, but it does not by itself prove that one group carried out all three attacks.
Does The Hack Threaten Binance’s Solvency?
Sean Farrell, head of digital asset strategy at Fundstrat Global Advisors, an investment research firm, said the attack does not currently appear to create significant solvency risk for Binance. “The most important takeaway for markets is that this does not currently appear to create meaningful solvency risk for Binance,” he said.
Farrell estimated that around $3.3 billion in assets remained unfrozen. Assuming frozen stablecoins are eventually returned, Binance’s SAFU emergency fund, worth approximately $1.2 billion, could cover roughly a third of the remaining losses. The balance would come from the exchange’s own funds.
He said it is important to see how quickly Binance allows withdrawals to start again and if there are any orderly outflows. If customers have a shortfall of assets, the exchange may be forced to sell its reserves which could cause panic selling in crypto. Farrell added: “I do not think that is the setup we are dealing with, but the key tell will be how quickly withdrawals resume and whether outflows stay orderly.”
Bitcoin Falls As Experts Flag Confidence Risk
The price of Bitcoin fell about 5% after the news, dropping below $77,000 but since then BTC has recovered back to around $78,500, at the time of writing this article.
Sean Foley, a crypto-markets expert at Macquarie University in Sydney, said Binance is one of the largest centralized exchanges. He said a blow to confidence in it risks shocking many retail investors and could dampen crypto prices.
Foley said the attack highlights the risks of centralized exchanges and could push more traders toward decentralized alternatives. In his words: “Any assets held at a centralized exchange are only as safe as the exchange itself, and the larger the exchange’s holdings, the larger a target it becomes.”
Calls For Stronger Cybersecurity Standards
Chris Perkins, head of Franklin Crypto at asset manager Franklin Templeton, said the hack underscores the need for stronger cybersecurity standards and greater coordination among governments. Speaking in a television interview, he said the industry must address its cybersecurity challenges to reach its full potential. He called for stronger defenses and policies that hold cybercriminals accountable.
“We need to make sure standards are incredibly high, but we have to really focus on the criminals,” Perkins said. He pointed to the regulatory coordination among G20 countries after the global financial crisis as a possible model for international cooperation. He also said AI could help improve cybersecurity by identifying and addressing vulnerabilities, even as both attackers and defenders use the technology.
A Record Theft In Context
The Binance breach dwarfs the $1.5 billion Bybit hack of 2025, the previous record. For comparison, TRM’s 2026 Crypto Crime Report found that cybercriminals stole $2.87 billion in crypto assets across nearly 150 hacking incidents in 2025. Investigations are continuing. Binance has said further technical details will follow once they are verified.
Stay informed with the latest trends in Web3, blockchain innovation, and cybersecurity updates at 3verseTV
You need to login in order to Like



Leave a comment