
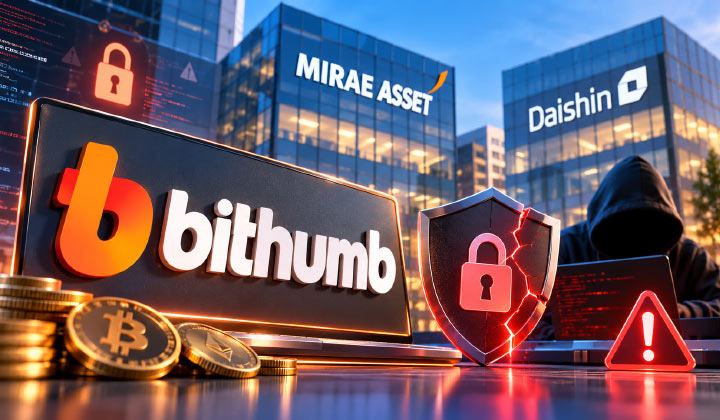
- An outsider broke into an employee mobile communication and work system at Bithumb on October 27, extracting personal information; the exchange reported the incident to KISA and PIPC.
- Bithumb confirmed that its trading platform is separate from the compromised system and that customer virtual assets cannot be accessed through it.
- FSS Governor Lee Chan-jin confirmed hacking incidents across major South Korean financial investment companies, including Daishin Securities, which saw 38,490 customers’ personal and credit data leaked.
- Mirae Asset blocked abnormal access to its web systems; investor information was not affected. The October 27 attacks followed an earlier wave of cyberattacks on 16 South Korean financial firms on October 14.
An outsider broke into an employee mobile communication and work system at South Korean cryptocurrency exchange Bithumb on October 27, extracting personal information belonging to staff. The exchange reported the incident to the Korea Internet and Security Agency (KISA) and the Personal Information Protection Commission (PIPC).
South Korea’s Second-Largest Crypto Exchange Bithumb Confirms Security Breach
According to Yonhap News Agency, South Korea’s second-largest cryptocurrency exchange, Bithumb, confirmed that an unauthorized external party accessed its internal mobile groupware system, resulting in a personal data leak. The exchange discovered the incident on October 27 and is investigating whether customer information was compromised.
Two other South Korean financial institutions, Mirae Asset Global Investments and Daishin Securities, were also confirmed to have suffered cyber intrusions. Daishin Securities disclosed that the personal and credit information of 38,490 customers had been leaked. South Korea’s Financial Supervisory Service (FSS) is investigating the incidents.
— Wu Blockchain (@WuBlockchain) October 28, 2026
Bithumb said its trading platform is entirely separate from the compromised communication system and stated that customer virtual assets cannot be accessed through the affected infrastructure, meaning no crypto funds were lost.
FSS Governor Confirms Broader Financial Sector Attacks
Financial Supervisory Service Governor Lee Chan-jin confirmed hacking incidents across what he described as major financial investment companies. The breach at Bithumb was not an isolated event.
🚨BREAKING:
Bithumb admits internal data leak after cyber intrusion; Daishin Securities and Mirae Asset also hit, exposing tens‑of‑thousands of personal records. No theft reported yet, but regulators are probing potential links across South Korea’s crypto and finance sector. https://t.co/xLFuMelxCA— Pulse Alpha (@pulsealpha_) October 28, 2026
Daishin Securities disclosed that 38,490 customers’ personal and credit information was stolen in an outside attack. Mirae Asset said it detected and blocked abnormal access attempts to its web systems and confirmed that investor information was not compromised. South Korean financial authorities have placed the sector on heightened alert.
October 14 Precedent & Bithumb’s February Lapse
The October 27 attacks came less than two weeks after a separate wave of cyberattacks on October 14 that targeted 16 South Korean financial firms simultaneously. That earlier campaign had already prompted regulators to warn the sector about coordinated intrusion activity.
In February 2026, Bithumb faced criticism once more after it mistakenly credited 620,000 BTC roughly $40 billion to customer accounts, rather than the 620,000 Korean won that was intended.
This mistake was attributed by CEO Lee Jae-won to a vulnerability in their internal control system. While unrelated to the October hack, the February incident raised questions about operational standards at the exchange.
Stay informed with the latest trends in Web3, blockchain innovation, and cybersecurity updates at 3verseTV
You need to login in order to Like



Leave a comment