
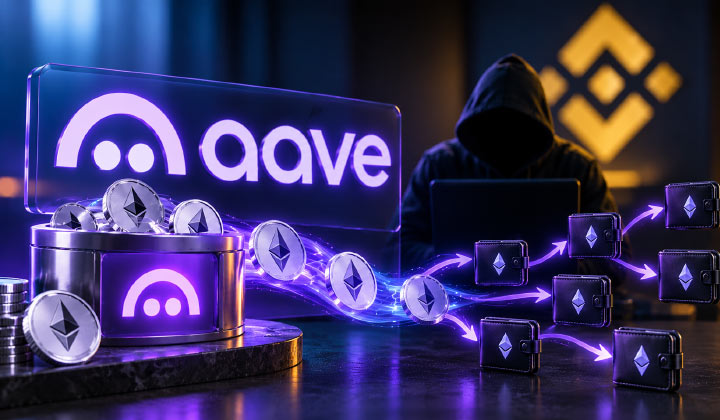
- The Binance hacker deposited approximately $60 million in stolen USDT as collateral on Aave and borrowed $44.6 million in Ether against it, using the DeFi lending protocol as a mixing service to convert a frozen stablecoin into a harder-to-trace token
- Aave’s permissionless design means no party could block the deposit, refuse the collateral, or freeze the borrowed ETH once the transactions were confirmed on-chain
- The borrowed ETH was subsequently moved through Uniswap, adding a further layer of obfuscation to the trail
- Since Tether subsequently blacklisted the stolen USDT addresses, the $60 million in collateral on Aave is now frozen and unusable but the attacker may retain the $44.6 million in ETH, paying an effective cost of $15.4 million for the conversion
Deposit Stolen USDT, Borrow Fresh ETH
In addition to fragmenting the funds across 19 wallets, the hacker of Binance employed the Defi lending strategy in order to change stable coins into something harder to freeze.
We’re aware of reports of a potential incident affecting Binance-affiliated wallets.
Aave’s contracts are unaffected, and positions remain overcollateralized. As a precaution, all DAO-operated markets across V3 and V4 have been frozen.
The freeze pauses new deposits and borrows, and users can still withdraw and repay their existing positions.
— Aave (@aave) October 29, 2026
It was found out that the hacker made use of Aave, which is a decentralized lending protocol, by depositing around $60 million of the stolen USDT as a collateral and borrowing $44.6 million of Ether using the USDT collateral. The overcollateralized system of Aave requires borrowers to lock up a higher value of funds compared to what they borrow.
DeFi’s Permissionless Nature As A Liability
The technique exploits a core feature of decentralized finance: once a transaction is submitted to a public blockchain and confirmed, no party can reverse or block it. Aave cannot prevent a deposit, refuse collateral, or freeze borrowed ETH after the fact.
Binance hack was the greatest robbery of all time https://t.co/qCvl8apqbU
— PsyopAnime (@PsyopAnime) October 30, 2026
The attacker effectively used a legitimate DeFi protocol to launder funds depositing a blacklisted asset as collateral and withdrawing a different, less-regulated token. The borrowed ETH was then moved through Uniswap, adding a further layer of obfuscation to the trail.
What Happens To The Collateral Now
Since Tether subsequently blacklisted the stolen USDT addresses, the $60 million in collateral on Aave is now effectively worthless the USDT cannot be moved or liquidated. The borrowed ETH, however, is already in the attacker’s control.
This creates a situation where the attacker may walk away with $44.6 million in ETH at the cost of abandoning $60 million in frozen USDT. The incident highlights how DeFi protocols, designed to be neutral and permissionless, can be weaponized to obscure the origin of stolen funds a tactic increasingly documented in post-hack blockchain analyses.
Stay informed with the latest trends in Web3, blockchain innovation, and cybersecurity updates at 3verseTV
You need to login in order to Like



Leave a comment