
- Binance estimates the October 29, 2026 breach at about $6.3 billion, with roughly $3 billion frozen on-chain, making it the largest crypto theft on record.
- Binance says it will cover all losses from its SAFU emergency fund and company reserves, and expects withdrawals to resume within 48 hours.
- Circle, Tether, Ripple and other issuers froze stolen stablecoins, while rival exchanges and DeFi protocols moved to block hack-linked addresses.
- TRM Labs and Chainalysis attribute the attack to North Korea’s TraderTraitor group. Binance has not named an attacker, and no government has confirmed the attribution.
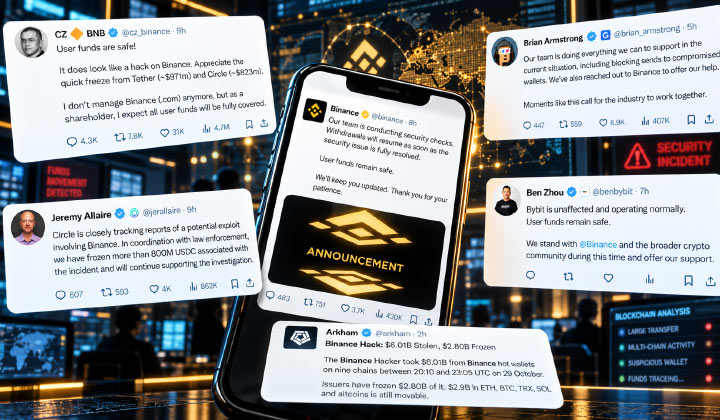
Binance, the world’s largest cryptocurrency exchange by trading volume, suffered a security breach on October 29, 2026. The company puts the impact at about $6.3 billion, the biggest crypto theft ever recorded. Binance says it will cover all losses through its Secure Asset Fund for Users (SAFU) and company funds. Circle, Tether and others froze billions in stablecoins. TRM Labs and Chainalysis say North Korea’s TraderTraitor group is likely responsible. More than 70 exchanges, executives, issuers, investigators and analysts have since responded publicly.
How The Binance Hack Unfolded
Blockaid, a blockchain security firm, traced the attack to a transaction submitted at 20:20:59 Coordinated Universal Time (UTC) on October 29. It carried 50 EIP-7702 authorizations aimed at the hot wallet labeled “Binance 14.” EIP-7702, short for Ethereum Improvement Proposal 7702, lets an ordinary Ethereum wallet pass control of its actions to smart contract code. A hot wallet is an internet-connected wallet that an exchange uses for day-to-day withdrawals.
Large outflows started around 20:24 UTC, which was 01:54 India Standard Time (IST) on October 30. A single transaction moved about 167,464 Ether (ETH), roughly 1.615 billion Tether (USDT) and dozens of other tokens to a newly created address.
The key public moments that followed, all in UTC:
| Time (UTC) | Who | What Happened |
| Oct 29, 20:32 | Spreek, on-chain researcher | Flagged a “possibly massive Binance hack” funded through Tornado Cash |
| Oct 29, 21:15 | Changpeng Zhao (CZ) | Said “it does look like a hack on Binance” |
| Oct 29, 21:18 | Jeremy Allaire, Circle | Said Circle froze more than 800 million USDC |
| Oct 29, 21:25 | Paolo Ardoino, Tether | Said Tether froze more than 1.567 billion USDT |
| Oct 29, 22:15 | Binance | Said withdrawals would resume once the issue was resolved |
| Oct 30, 00:04 | Yi He, Binance | Said Binance “will cover all hacking losses” |
| Oct 30, 01:19 | Brian Armstrong, Coinbase | Offered help and began blocking sends to compromised wallets |
| Oct 30, 02:25 | Binance | Published initial findings and the $6.3 billion estimate |
| Oct 30, 04:17 | Yi He, Binance | Said withdrawals should resume within 48 hours |
| Oct 30, 04:51 | ZachXBT | Linked Binance and Bitget hack funds through THORChain |
What Binance & Its Leaders Said
Binance’s first post on X said its teams were “aware of reports of a potential security issue” and had not confirmed any effect on user funds. The post was later edited to say user funds were “completely safe.” At 02:25 UTC on October 30, the exchange pointed to a compromised DevOps engineer’s laptop as the likely entry point and promised to cover every loss using SAFU, an emergency reserve it set up in 2018, along with company funds.
Changpeng Zhao, widely known as CZ, is Binance’s co-founder and former Chief Executive Officer (CEO). He wrote that “user funds are safe” and that the activity “does look like a hack on Binance.” He thanked Tether and Circle for freezing about $971 million and $823 million, respectively. As a shareholder, he said, he expects all user funds to be fully covered. At 21:36 UTC he also thanked Circle CEO Jeremy Allaire directly.
CZ later replied to an estimate from 0xngmi, the pseudonymous founder of analytics platform DefiLlama. 0xngmi put Binance’s net loss after the stablecoin freezes at about $1 billion, or 0.69% of the roughly $144 billion in assets it holds in custody. CZ said the loss might be slightly higher but would be covered.
Co-CEO Richard Teng wrote early on October 30: “I want to be direct: user funds remain SAFE.” He added that security teams were reviewing all information urgently.
Co-founder and co-CEO Yi He posted at 00:04 UTC: “User funds are safe. Binance will cover all hacking losses.” In a service update at 04:17 UTC, she said Binance expects to resume withdrawals within 48 hours and that deposits continue to work normally.
Binance.US was unaffected. In Thailand, Binance TH, operated by Gulf Binance, paused crypto deposits and withdrawals for a security check. It said Thai customer assets were safe because its cold wallets are held separately.
Stablecoin Issuers & Networks Freeze Funds
Circle co-founder and CEO Jeremy Allaire said the company had “frozen more than 800M USDC associated with the incident,” working with law enforcement. USD Coin (USDC) is Circle’s dollar-pegged stablecoin.
Seven minutes later, Tether CEO Paolo Ardoino said Tether “froze more than 1.567B USDT related to a potential Binance exchange hack.” He added that protecting the industry and its partners was the company’s top priority. CZ replied to the post and called Tether a “life saver.”
Jack McDonald, senior vice president of stablecoins at Ripple, said the company was “actively freezing affected funds” held in Ripple USD (RLUSD) and coordinating with relevant parties. Yi He put the Ripple freeze at about $200 million.
Zach Witkoff, co-founder and CEO of World Liberty Financial, confirmed that about $27 million in USD1, the company’s stablecoin, was frozen. Custodian BitGo worked with World Liberty Financial to freeze the stolen USD1 and about $2 million in WLFI tokens.
Vincent Chok, founder and CEO of First Digital, confirmed at 01:19 UTC that First Digital USD (FDUSD) taken in the attack had been frozen.
The Arbitrum Security Council is an elected body that can take emergency action on the Arbitrum network. It froze about $30.5 million held by the attacker, made up of 74.56 million Arbitrum (ARB) tokens and 8,425 ETH.
How Exchanges Around The World Responded
India
CoinDCX, India’s largest crypto exchange, switched its futures market to reduce-only mode. It cited “recent developments impacting a global liquidity provider.” A spokesperson later confirmed the provider was Binance.
In light of recent developments impacting a global liquidity provider, CoinDCX Futures trading is temporarily in Reduce-Only mode as a precaution.
What this means for you:
– No new positions: You can’t open new positions in the futures market.
– No position increases: You can’t add quantity or increase the size of your existing open positions.
– Active position management: You can still add or reduce margin on your existing positions.
– Reducing positions: You can close or reduce your open positions anytime.
– Deposits & withdrawals: Your funds remain safe and deposit/withdrawals work seamlessly without any issue.We’ll keep sharing updates through our official channels.
— CoinDCX (@CoinDCX) October 30, 2026
Traders could not open new positions or enlarge existing ones. Deposits, withdrawals and customer funds were not affected. However, CoinDCX later announced on X that Futures trading is now fully operational across all markets, except 4 tokens (SOPH, ERA, GTC, LA) that remain in Reduce-Only mode as a precaution.
Update: Futures Trading has resumed
We are pleased to inform you that Futures trading is now fully operational across all markets, except 4 tokens that remain in Reduce-Only mode as a precaution.
Following recent developments involving our global liquidity provider, our Risk team continues to monitor these 4 tokens for potential market manipulation and unusual volatility.
List of 4 tokens in Reduce – Only mode for now (INR & USDT Pairs):
– SOPH
– ERA
– GTC
– LAYour safety remains our priority. Thank you for your patience and trust.
https://t.co/jGbUYmOLse
— CoinDCX (@CoinDCX) October 30, 2026
United States
Brian Armstrong, co-founder and CEO of Coinbase, wrote at 01:19 UTC that the US exchange was “blocking sends to compromised wallets” and had contacted Binance to offer help. “Moments like this call for the industry to work together,” he said. He added that customer protection should come first “regardless of which platform they use.” Coinbase separately said it was unaffected and watching the situation. Conor Grogan, a senior director at Coinbase, estimated the outflows at up to $5.8 billion.
South Korea
Upbit, South Korea’s largest crypto exchange, issued a notice at about 7:46 a.m. Korea Standard Time (KST) on October 30, or 22:46 UTC on October 29. It was titled “Notice Regarding Digital Asset Withdrawal Restrictions to Binance Exchange.” Upbit said security incidents and signs of theft had been confirmed at Binance. It urged users to be extremely careful when withdrawing to Binance and said it might restrict such withdrawals to protect investors.
Bithumb, Coinone and DigitalX followed with their own notices warning users against withdrawals to Binance.
Global Exchanges
Bybit said it was aware of reports of “a security incident affecting multiple platforms,” but stated, “Bybit is not affected.” Trading and withdrawals stayed open. Co-founder and CEO Ben Zhou said the exchange was ready to support Binance. Bybit itself lost about $1.5 billion in a February 2025 hack that the Federal Bureau of Investigation (FBI) attributed to North Korea.
OKX founder and CEO Star Xu described the recent incidents at Bybit, Bitget and Binance as a wake-up call for every industry leader. He said security should not be a field of competition. He proposed shared standards, including security delays on large withdrawals to unverified addresses, industry-wide incident alerts and a shift to post-quantum cryptography. In a separate post, he praised Circle and Tether’s response and said freezes should happen “within minutes rather than hours or days.”
Bitget lost about $388 million in a hack on September 24. It said its platform was stable and that it stood with Binance, adding that security is a shared responsibility rather than a competition.
KuCoin said it knew of reports of an incident affecting several platforms and that its own services and user assets were not affected.
Kris Marszalek, co-founder and CEO of Crypto.com, said the platform was unaffected and was blocking addresses tied to the hack. He added that the company had reached out to Binance to offer help.
Investigators Trace The Money & Point To North Korea
Blockchain analytics firm TRM Labs attributed the attack to TraderTraitor, a North Korean state-sponsored hacking group, “based on robust onchain and offchain intelligence.” It traced about $6.36 billion leaving Binance-attributed wallets across 10 blockchains. The evidence, it said, points to a compromise of Binance’s hot wallet signing infrastructure. TRM senior investigator Nick Carlsen told The Wall Street Journal: “This was absolutely North Korea.”
Jonathan Levin, co-founder and CEO of Chainalysis, said in a post on X that the firm assesses the theft was “likely done by DPRK group TraderTraitor due to links to previous hack.” DPRK stands for the Democratic People’s Republic of Korea, North Korea’s official name. Chainalysis valued the theft at $5.912 billion at the time it happened, nearly four times the Bybit hack. A Chainalysis spokesperson told CNN the firm had “high confidence” North Korea was responsible.
On-chain investigator ZachXBT named the Lazarus Group, a North Korean state-backed hacking unit, as the likely attacker, and linked the Binance funds to the $388 million Bitget exploit through THORChain, a cross-chain swap protocol.
Ido Ben-Natan, co-founder and CEO of Blockaid, said the evidence pointed to “key misuse” rather than key theft. In other words, attackers likely tricked or took over a signing system without pulling out the private key. He called the attack “very, very similar” to the Bybit hack.
Ben-Natan also gave a fuller assessment: “This is the biggest crypto hack in history. Our analysis shows at least $3.5 billion moved out of Binance hot wallets on Ethereum, Arbitrum, Optimism and Avalanche in under an hour, more than double the Bybit theft in February 2025, and on-chain trackers are reporting further outflows on Bitcoin and Tron.”
He said the attacker effectively reprogrammed a major Binance Ethereum hot wallet so that one operator could drain it, including any new deposits, and used that access again more than an hour later. According to Ben-Natan, the attack was planned well in advance. The attacker funded the operation through Tornado Cash and rehearsed the same takeover on test wallets hours earlier, all visible on-chain. He said Tether and Circle froze roughly $2.4 billion quickly, and that Blockaid is still tracing the rest.
Other analysts offered their own estimates:
- Miguel Morel, CEO of Arkham Intelligence, said wallets labeled “binance-hacker-1029” held about $5.84 billion and that the attack appeared to be continuing.
- Taylor Monahan of the security alliance SEAL 911 put early losses at more than $2 billion and as high as $5.5 billion.
- Analytics firm Glassnode estimated about $5.3 billion was withdrawn, including $1.66 billion in USDT, $1.45 billion in Bitcoin and $763 million in USDC.
- Shen Yu, co-founder of Cobo and F2Pool, estimated abnormal transfers across Ethereum, TRON and Bitcoin at about $5.8 billion at their peak.
- On-chain analyst Emmett Gallic tracked more than $5 billion leaving Binance addresses.
- Protocol engineer Justin Kalland flagged more than $2.5 billion drained from a single hot wallet funded through Tornado Cash.
Lookonchain, an on-chain tracker, reported that the attacker swapped UNI, ENA, PEPE, LINK, AAVE, ONDO and WLD tokens for 70,480 ETH, worth about $158.25 million. At security firm SlowMist, Chief Information Security Officer 23pds said he leans toward a private key leak. Founder Cosine linked the hacker’s fund flows to addresses tied to the early 2025 Phemex theft.
Mark Karpeles, CEO of Karpeles Lab and former head of Mt. Gox, said Binance appeared to have spread its assets across several systems, which limited how much one breach could reach. An analyst at Pangolin Intelligence told CNN that “the cat and mouse game has barely begun.”
Binance has not publicly named an attacker, and no government has confirmed the attribution.
DeFi Protocols Act To Limit Spillover
Aave, a decentralized finance (DeFi) lending protocol, froze new deposits and borrowing across most of its V3 and V4 markets. Wallets linked to the hack had borrowed about $44.6 million in ETH against roughly $60 million in USDT between 20:58 and 21:01 UTC. Analysts MonetSupply and cryptoblaney were among the first to flag the activity. Aave said its contracts were unaffected and all positions remained overcollateralized.
Kamino, a Solana-based lender, said it was unaffected but paused borrowing in its SOL/BTC market as a precaution. 1inch, a decentralized exchange (DEX) aggregator, said it worked with ZeroShadow, SEAL 911 and TRM Labs to block exploit-linked addresses across its app, wallet and application programming interface (API) within the first hour.
Ethena, issuer of the USDe synthetic dollar, said the collateral it holds on exchanges sits with off-exchange custodians. It put its unrealized profit and loss exposure to Binance at about $8.8 million. At 04:25 UTC, Ethena published a proof of reserves showing USDe overcollateralized by more than $60 million, above 101%.
Lido, a liquid staking protocol, said its stETH token was unaffected. Aethir, a GPU network, said it had no exposure but was auditing its systems. The Sandbox, a metaverse game, said it was working with Binance and warned users about fake “claim” messages.
Market Makers & Analysts Assess The Damage
Evgeny Gaevoy, CEO of market maker Wintermute, said its exposure to Binance was “less than 20% of net equity,” with no operational disruption expected. GSR CEO Xin Song put the firm’s exposure below 5% of net equity. Aravind Srinivasan, head of GSR’s systematic over-the-counter (OTC) business, called it “the biggest hack in history.” He said Bitcoin spot spreads on Binance were five times wider than normal.
Kevin March, co-founder of JPEG Trading, said, “This is unprecedented.” The same attack on any smaller crypto business, he added, “would’ve been catastrophic.”
Geoff Kendrick, head of digital assets research at Standard Chartered, said prices may stay under pressure until frozen assets are released. James Seyffart, an analyst at Bloomberg Intelligence, said the amount would be a meaningful hack on the largest crypto exchange. Tim Sun, senior researcher at HashKey Group, said investors may reassess how safe it is to hold assets on centralized exchanges.
Julio Moreno, head of research at CryptoQuant, noted that Bitcoin was testing its 365-day moving average near $77,406.
Other Voices From The Industry
Yishi, founder of OneKey, said the Binance and Bybit incidents show that attackers can steal assets by compromising signing approval systems even when private keys stay safe. Simon Gerovich, CEO of Metaplanet, said all of the company’s Bitcoin is held in cold wallets with regulated custodians, and he voiced support for Binance. Gerovich has previously spoken about custody risk following the Coldcard exploit in August.
Elon Musk, CEO of Tesla and SpaceX, warned that superintelligent artificial intelligence (AI) agents could one day carry out similar attacks to secure funds for themselves. Samson Mow, CEO of JAN3, replied to Ardoino’s post with “Tether saving Binance,” while the security research account vx-underground highlighted the freeze to its followers.
What Happens Next
Binance has promised a full post-mortem and an updated proof of reserves once its investigation is finished. Yi He’s 48-hour window for resuming withdrawals runs to about 04:17 UTC on November 1. Much of the unfrozen money sits in ETH and Bitcoin that no issuer can freeze.
Stay informed with the latest trends in Web3, blockchain innovation, and cybersecurity updates at 3verseTV
You need to login in order to Like



Leave a comment