
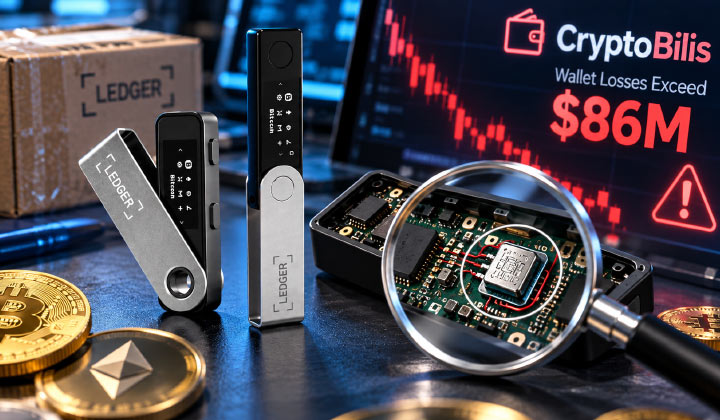
Ledger has confirmed that a device belonging to a user affected by the CryptoBilis incident contained an “unauthorized hardware implant,” adding evidence of possible physical tampering to an ongoing investigation into substantial cryptocurrency losses across Southeast Asia.
In an update published on October 10, Ledger said the implant had been identified in one affected user’s device. The development follows images shared by former Mt. Gox chief Mark Karpelès showing a distrustful component concealed inside a Ledger device. The confirmation strengthens the physical-tampering theory but does not establish that the insert caused every reported loss or that all Ledger devices are affected.
Situation Update: Ledger can confirm that one of the impacted users’ devices contained an unauthorized hardware implant. Ledger is reaching out to impacted users as part of the ongoing investigation. If you have information regarding the investigation, please reach out to Ledger’s bounty program: bounty@ledger.fr. As a measure of precaution CryptoBilis confirmed it has ceased sales of all hardware wallet inventory until the investigation is concluded. Ledger is in active communication with CryptoBilis on next steps.
Ledger is working with the appropriate authorities to bring the bad actors to justice, and thanks @SEAL_911 for their collaborative support on the investigation. We have no indication that Ledger’s security infrastructure, systems or services have been compromised. As a reminder, Ledger recommends users who purchased a Ledger device from this reseller to not initiate set up if they have not yet done so. If you have set up your Ledger device, consider moving assets to a new Ledger signer (with a new seed).
Security is a constantly evolving landscape; Ledger is continuously adding security mitigations and is working on further, enhanced anti-tampering solutions.
Scammers often try to take advantage of incidents like this. Rely only on official Ledger channels for updates, and remember: Ledger will never ask for your 24-word recovery phrase.
For assistance or questions, contact Ledger customer support through our official channels: https://t.co/PeTo6Z7l84
— Ledger Support (@Ledger_Support) October 10, 2026
Losses Estimated At Over $86M
The incident has been associated with reported cryptocurrency losses exceeding $86 million. Blockchain analytics firm Bitquery estimated that about $92.9 million was lost in 311 wallets in the five blockchains. However, these are rough estimates, since the final loss amount has yet to be officially confirmed by Ledger.
Investigators are still determining how many devices were exploited and whether they are in any way related to the discovered hardware implant and the drain of the crypto-wallets.
What Affected Customers Should Do
Ledger advised customers who purchased devices through CryptoBilis within the 90 days preceding its warning and have not yet activated them not to begin setup. Customers who have already configured such devices should consider moving their assets to a new Ledger signer with a newly generated recovery seed, following the company’s official instructions.
CryptoBilis Halts Sales As Probe Continues
CryptoBilis has suspended sales of its hardware-wallet inventory while the investigation continues. The reseller operates across Southeast Asian markets, including Indonesia, Malaysia and the Philippines. Ledger said it was communicating with the reseller and working with appropriate authorities, with assistance from crypto security-response collective SEAL 911.
Ledger also said it had no indication that its own security infrastructure, systems or services had been compromised. The company is continuing to develop additional anti-tampering measures. Users are urged to follow official support channels and never disclose their 24-word recovery phrase to anyone claiming to offer emergency assistance.
Stay informed with the latest trends in Web3, blockchain innovation, and cybersecurity updates at 3verseTV
You need to login in order to Like



Leave a comment