
On-chain investigator ZachXBT has exposed the online identities of five alleged money launderers involved in moving funds stolen in the $387.5 million Bitget hack. In a September 28 post on X, he claimed that the individuals were Chinese illicit actors working on behalf of suspected North Korean hackers.
The disclosure revealed that the operators had openly sought help in public Discord and Telegram support channels after encountering problems with cryptocurrency swaps and withdrawals. ZachXBT also shared transaction records linking the alleged launderers to the movement of stolen funds across multiple blockchains.
BREAKING: Chinese illicit actors laundering funds from the $387M Bitget exploit on behalf of the alleged DPRK attackers are openly asking for support with orders in public Discord servers and Telegram channels of services they use.
Notably, Alias 4 (below) was also seen… pic.twitter.com/KfdTo51M2o
— ZachXBT (@zachxbt) September 28, 2026
The five individuals were identified by their online aliases: Cc, jack, Melon, lolo/Marin and HELP ME. According to ZachXBT, their public conversations with support teams provide additional evidence that could help investigators trace the stolen cryptocurrency.
Screenshots accompanying his post show the alleged operators seeking assistance with delayed XRP-to-Bitcoin swaps, refunded transactions and missing Bitcoin payments. A blockchain transaction flow chart also connects wallets associated with the Bitget hack to THORChain, a decentralized protocol that allows users to exchange cryptocurrencies across different blockchains.
ZachXBT further claimed that one of the alleged launderers, lolo/Marin, was involved in moving funds stolen from Kelp DAO in April 2026. That attack resulted in losses of approximately $292 million and was subsequently linked by blockchain investigators to TraderTraitor, a North Korean hacking group associated with the Lazarus Group.
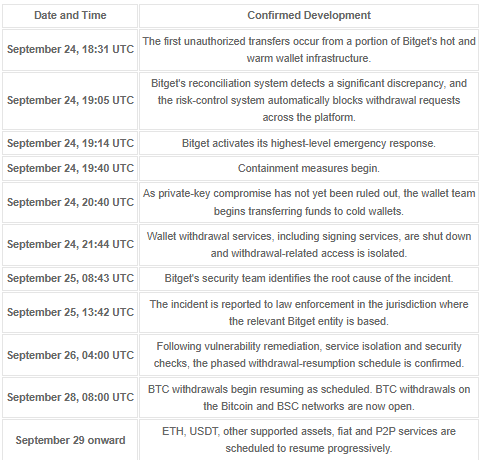
The latest disclosure follows the September 24 attack on Bitget, which initially reported losses of $351.6 million. The exchange later revised the figure to approximately $387.5 million after identifying additional unauthorized transfers.
Source: Bitget.com
Bit get has said the attackers exploited a vulnerability in a third-party security product to obtain high-level internal credentials and issue fraudulent withdrawal instructions. The exchange maintains that its private keys and cold wallets were not compromised.
Investigators believe the stolen assets are being moved between blockchains and converted into Bitcoin before entering privacy services such as Wasabi Wallet, making them harder to trace.
The incident has also sparked a dispute between Bitget and THORChain. Bitget has asked the decentralized protocol to block wallets associated with the attackers, but THORChain has declined, citing its permissionless design.
Although blockchain investigators have identified similarities with previous North Korean cyberattacks, no government has formally attributed the Bitget breach to North Korea. The identities and alleged activities disclosed by ZachXBT have not been independently verified.
Bitget has begun restoring withdrawals in phases, starting with Bitcoin on September 28. Ethereum and USDT withdrawals are scheduled to follow, with remaining services expected to resume by October 2. The exchange says its User Protection Fund will cover the losses and has announced a 5% bounty for assistance that leads to the freezing or recovery of stolen assets.
Stay informed with the latest trends in Web3, blockchain innovation, and cybersecurity updates at 3verseTV
You need to login in order to Like



Leave a comment