
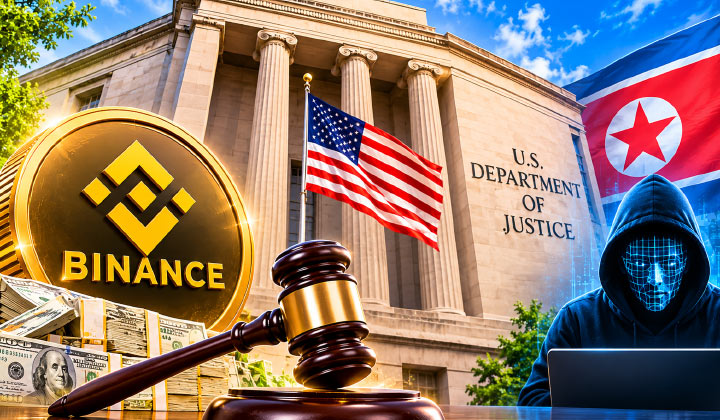
- The US Department of Justice has obtained court approval to seize or freeze more than $1.2 billion linked to the Binance hack.
- The hack has been attributed to a North Korean group known as TraderTraitor.
- The DOJ has also seized infrastructure used in a separate deepfake scam that allegedly stole more than $400 million in cryptocurrency.
US Authorities Target Stolen Funds From Binance
The US Department of Justice (DOJ) has taken steps to recover over $1.2 billion of cryptocurrency which was stolen from Binance. The DOJ has obtained a court order to seize or freeze the funds as part of broader efforts to locate assets related to the attack. Over $2.7 billion has been frozen so far through working with both public and private sectors.
The DOJ have stated that the attack was carried out by a North Korean hacking group known as TraderTraitor. The group is reported to have stolen over $6 billion from the exchange around October 29. Investigators are now tracking the movement of the funds as hackers try to move the stolen assets using crypto bridges, mixers and exchanges.
Following an initial estimate of losses at around $6.3 billion, Binance had reserved funds to cover the losses. However, it has stated that it has now covered the assets and has released an updated proof of reserves document.
Crypto Stolen Using Deepfake Video Calls
In another case, the DOJ has seized cloud infrastructure being used by a North Korean campaign known as FaceStealer. The FBI have stated that this has led to over $400 million worth of crypto being stolen over the last 18 months.
The attackers would use stolen online accounts to invite victims into video calls where they would use pre-recorded videos or deepfakes of people they know. They would then feign technical issues and ask users to install malicious software.
This would allow them to steal cryptocurrency and access further systems. In some cases they would wait months or over a year before attempting to steal.
Contact lists were also stolen. This allowed them to target more people using the compromised accounts. Those targeted could include open-source software developers. The FBI have seized over 900 webcam recordings from victims and have released guidance for those who may have been affected.
This latest case shows that crypto theft is not limited to attacks on exchanges and wallets. Criminal groups are using personal connections, false identities and familiar communication methods to deceive individuals into giving up access to their systems.
Stay informed with the latest trends in Web3, blockchain innovation, and cybersecurity updates at 3verseTV
You need to login in order to Like



Leave a comment