
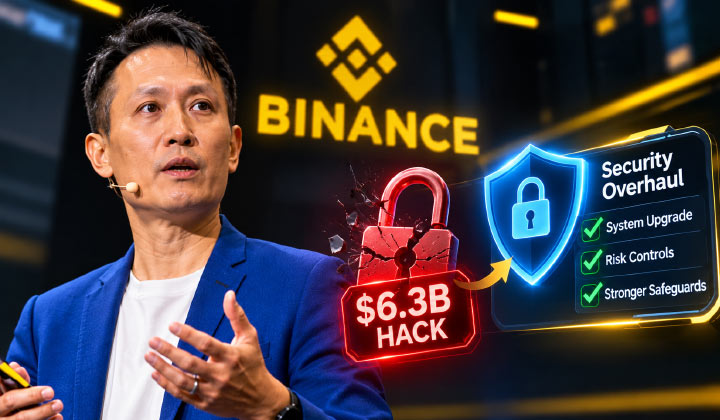
- The Binance hack was a coordinated multi-month campaign beginning in June 2026 with a compromised AI coding tool downloaded via Homebrew.
- A second engineer was targeted in September via a fake recruiter coding challenge, installing malware on their device.
- Attackers exploited EIP-7702 to continue unauthorized transfers even after Binance attempted to suspend withdrawals.
- Co-CEO Richard Teng described the attack as “a months-long campaign,” $2.85 billion was frozen and 98% of assets have been replenished.
A Months-long Chain Of Infiltration
The Binance crypto exchange suffered a months-long coordinated hacking campaign in June 2026. It started when a Binance engineer unknowingly installed a malicious version of an AI code tool distributed via the Homebrew package manager. The malicious code provided the hackers with a foothold.

https://t.co/sU9dUqLQDH
— Binance (@binance) November 3, 2026
Social Engineering Deepens The Breach
In September, threat actors used a fake recruiter to target another Binance engineer. This time they posed as a coding challenge during the recruitment process. The engineer completed the challenge unknowingly running malware on their machine.
The malware was silently installed on their laptop. By October 20th the hackers were using the two infected machines and the Binance AI code tool to gain access to two other engineers. They stole credentials to deploy onto Binance’s production environment.
Wallet Infrastructure & EIP-7702 Exploited
On October 29th, the hackers deployed malicious code onto Binance’s wallet infrastructure. They gained access to the wallet signing service.
They used EIP-7702 which is an Ethereum improvement proposal that allows account abstraction to continue stealing funds. Binance had tried to stop the hackers from withdrawing funds but due to the multiple-party computation wallet they have the issue of being unable to quickly revoke the signing rights.
This meant they couldn’t stop the unauthorised transactions taking place. In total, $6.3 billion, with $2.85 billion worth of assets were impacted.
BREAKING: 🎙💥 “This was a highly sophisticated, multi-month campaign, and FBI has attributed it to North Korea,” says Binance co-CEO Richard Teng.
🗞️ “They used a combination of fake recruitment interviews, malicious software disguised as developer tools and AI techniques.” https://t.co/7Q2nTXbMxl
— Bitcoin.com News (@BitcoinNews) November 3, 2026
Co-CEO Richard Teng stated: “This wasn’t one mistake, this was a months-long campaign.” Binance has replaced 98% of the assets impacted however it was a complete change to their security processes and third party screening.
Stay informed with the latest trends in Web3, blockchain innovation, and cybersecurity updates at 3verseTV
You need to login in order to Like



Leave a comment