
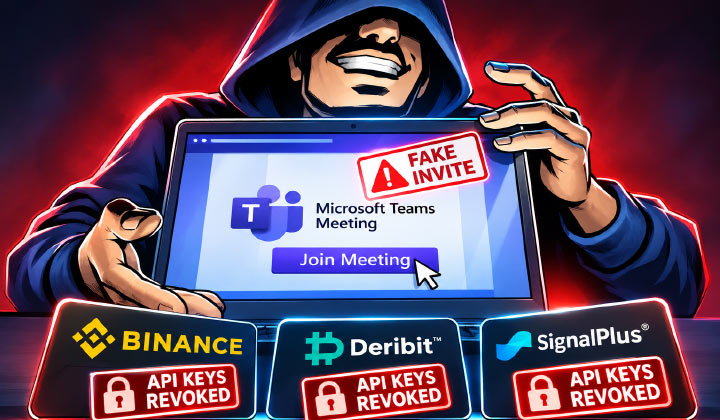
- Binance and Deribit revoked SignalPlus API keys after a cyberattack.
- SignalPlus reported losses below $82,000 and began reimbursing affected users.
- A fake Microsoft Teams invitation compromised a SignalPlus engineer’s computer.
Binance and Deribit removed API keys linked to SignalPlus on Thursday as a precaution after a security issue occurred. Both exchanges claimed their own systems were not harmed. Deribit said that trading, tracking, and automated functions through SignalPlus stopped working for users.
We have proactively revoked all Deribit customer API keys connected to SignalPlus as a precaution, after SignalPlus informed us they were experiencing a potential security concern. Deribit systems and data were not affected.
If you were using SignalPlus to trade on Deribit, all trading, monitoring, and automation has stopped as a result. You can check open orders, positions, and recent account activity directly on Deribit.
As always, only share your API keys with products you trust. When connecting, enable IP allowlisting for stronger security. If you intend to reconnect to SignalPlus, wait for official communication from their team before proceeding.
— Deribit (@DeribitOfficial) November 5, 2026
SignalPlus explained that the attack started when a Telegram account belonging to someone at a third-party tech company was hacked. That account sent a fake Microsoft Teams meeting request to an engineer. The engineer’s computer was then hacked.
The attacker stayed quiet for a while before using the engineer’s access to attack SignalPlus’s network early on Wednesday, according to the company.
If you use SignalPlus for any other exchange platform, it’s time to revoke all your API keys.
It is generally recommend that you do not store your API keys with any 3rd party platform. 🙏
(Deribit also/first reported this.)
— CZ 🔶 BNB (@cz_binance) November 5, 2026
SignalPlus said it found and stopped the attack. The total losses were then $82,000. The platform has started paying back users. It has paused services for now while it checks security and fixes problems. The company expects to start working in the next few days.
SignalPlus Admits API Security Oversight
The company admitted it had not used IP whitelisting for its exchange API access, taking responsibility for the mistake.
IP whitelisting restricts API connections to approved internet addresses, helping prevent unauthorized access. SignalPlus promised to tighten API access rules and boost internal security controls after the incident.
Binance co-founder Yi He also asked third‑party platforms that work with the exchange to check their security steps and look out for any activity.
SignalPlus Attack Follows Reported Binance Hack
The incident comes after Binance revealed a $6.3 billion hack on October 29. That hack reportedly used compromised employee computers.
According to Binance’s investigation, attackers impersonated recruiters. Tricked an engineer into downloading a malicious file that looked like a coding assignment. Binance then used the computer to reach other systems and break into Binance’s wallet infrastructure.
Yi He said on Tuesday that Binance had found and stopped 57 suspected North Korea‑linked cyber threats in 2026. Those threats used job interviews, malicious software packages, and attempts to steal login credentials.
Stay informed with the latest trends in Web3, blockchain innovation, and cybersecurity updates at 3verseTV
You need to login in order to Like



Leave a comment